+91 92891 11686 (Chat Only)

Certified in CyberSecurity CC

0 (0 Ratings)
The Certified in Cybersecurity (CC) certification from ISC2 is an entry-level cybersecurity credential designed for newcomers to the cybersecurity field. It validates foundational knowledge and skills across security principles, governance, identity and access management, networking and cloud security, security operations, and incident response. ISC2 specifically states that no work experience is required to pursue the CC certification.
No distractions. Just you!

Course Description

Key Takeaways
  • Understand fundamental cybersecurity concepts and security principles.
  • Learn risk management, governance, compliance, and cybersecurity controls.
  • Understand identity lifecycle management and logical access controls.
  • Develop foundational knowledge of network security, network architecture, and cloud security.
  • Understand data security, security operations, incident response, and asset protection.
  • Learn foundational security testing concepts.
  • Understand the security implications of AI across cybersecurity domains.
  • Prepare for the ISC2 Certified in Cybersecurity examination.
Course Outline

Domain 1: Security Principles — 24%

1.1 Understand cybersecurity concepts

  • Confidentiality
  • Integrity
  • Availability
  • Authentication, Authorization, Accounting (AAA)
  • Non-repudiation
  • Privacy

1.2 Understand risk management concepts

  • Risk management lifecycle
  • Risk management processes

1.3 Understand governance concepts

  • Regulations and laws
  • Frameworks and guidelines
  • Policies
  • Standards
  • Procedures

1.4 Understand cybersecurity controls

  • Technical controls
  • Administrative controls
  • Physical controls

1.5 Maintain professional and ethical conduct

  • Professional code of conduct
  • Due care and due diligence
  • ISC2 Code of Ethics

Domain 2: Security Governance — 17.3%

2.1 Plan Governance, Risk, and Compliance (GRC)

  • Purpose
  • Importance
  • Frameworks and tools

2.2 Understand redundancy

  • Business Continuity (BC)
  • Disaster Recovery (DR)

2.3 Understand security awareness

  • Organizational culture
  • Security leadership
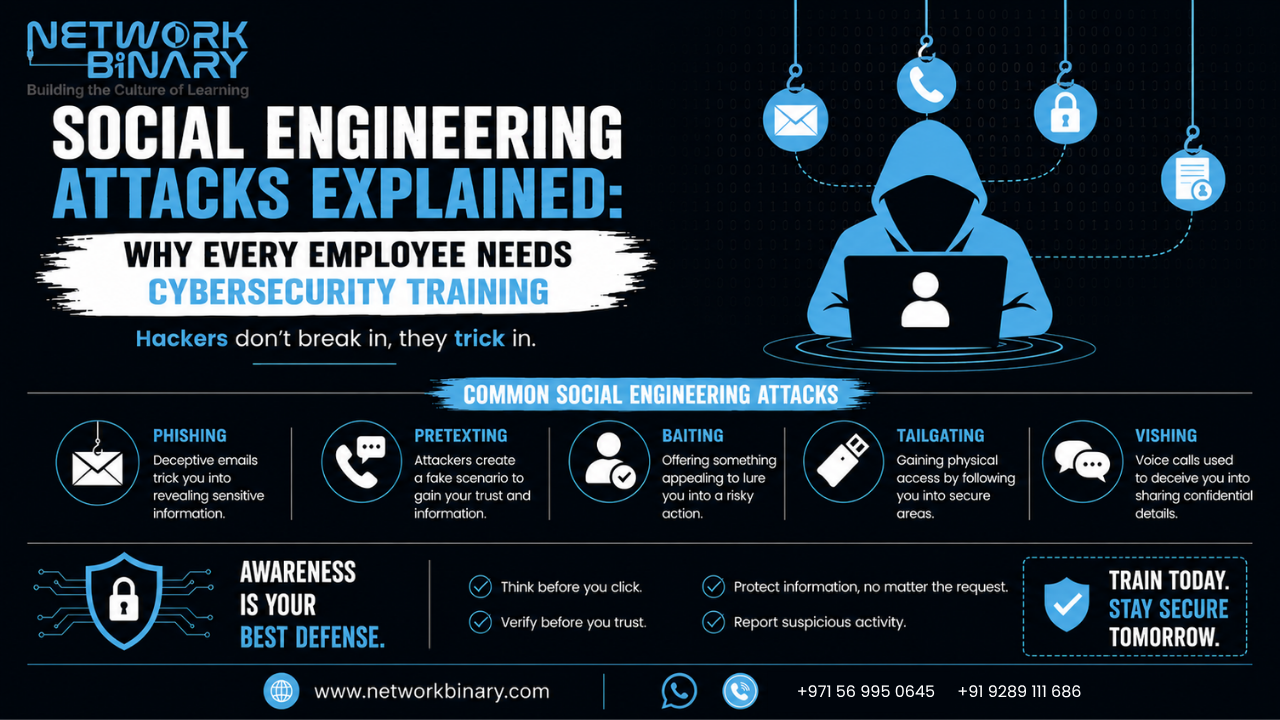
  • Social engineering
  • Password protection
  • Phishing

2.4 Measure cybersecurity effectiveness

  • Key metrics
  • Key Risk Indicators (KRI)
  • Dashboards
  • Scorecards
  • Reports

Domain 3: Identity And Access Management (IAM) Concepts — 20%

3.1 Understand identity life cycle management

  • Roles definition
  • Provision
  • Review
  • Deprovision
  • Frameworks and tools

3.2 Understand logical access controls

  • Principle of Least Privilege (PoLP)
  • Separation of Duties (SoD)
  • Access control models

Domain 4: Networking and Cloud Security Concepts — 21.3%

4.1 Understand network security

  • OSI model
  • TCP/IP model
  • IPv4
  • IPv6
  • Virtual Private Network (VPN)
  • Firewalls
  • Ports
  • Applications
  • Wireless security
  • Wi-Fi
  • Bluetooth
  • Embedded systems
  • Industrial Control Systems (ICS)
  • Internet of Things (IoT)

4.2 Understand network security architecture

  • Network segmentation
  • Firewall zones
  • VLANs
  • Micro-segmentation
  • Defense in Depth
  • Zero Trust (ZT)

4.3 Understand cloud security

  • Broad network access
  • Rapid elasticity
  • Measured service
  • On-demand self-service
  • Resource pooling
  • Cloud service models
  • Cloud deployment models
  • Shared security model
  • Cloud security roles and responsibilities

Domain 5: Security Operations and Incident Response — 17.3%

5.1 Understand data security

  • Data classification
  • Data labeling
  • Data masking
  • Data sanitization
  • Symmetric encryption
  • Asymmetric encryption
  • Hashing
  • Quantum-resistant cryptography

5.2 Understand security operations

  • Logging and monitoring security events
  • Security event triage
  • Incident use cases
  • Prioritization
  • Correlation
  • Threat actors
  • Threat actor types and motivations
  • Cyber threat intelligence
  • Threat frameworks

5.3 Understand Incident Response (IR)

  • Data handling policy
  • Incident Response Plan (IRP)
  • Incident Response exercises
  • Testing
  • Tabletop exercises

5.4 Understand asset protection

  • Asset lifecycle management
  • End-of-Life (EOL) software and devices
  • Configuration management
  • Change management

5.5 Understand security testing

  • Security readiness testing
  • Blue teaming
  • Purple teaming
  • Red teaming
  • Vulnerability scanning
  • Static analysis
  • Dynamic analysis
  • Threat modeling
  • Physical penetration testing
  • Phishing
  • Tailgating
  • Impersonation
Duration

2 Days

Exam Details

Certification: ISC2 Certified in Cybersecurity (CC)

Duration: 2 hours

Format: Computerized Adaptive Testing (CAT)

Questions: 100–125 multiple-choice and advanced item types

Who should attend
  • IT professionals.
  • Career changers transitioning into cybersecurity.
  • College students.
  • Recent graduates.
  • Individuals seeking an entry-level cybersecurity qualification.
  • Board-level executives seeking foundational cybersecurity knowledge.
Prerequisites

No formal prerequisites

Need Customized Curriculum?

GET A FREE DEMO CLASS

Choose Your Preferred Learning Mode

One-To-One Training

Personalized Schedule one-on-one Expert Guidance Private Session – Just You & the Instructor Guaranteed-To-Run Tailored for Your Success

ONLINE TRAINING

Learn Anytime, Anywhere Self-Paced & Interactive Budget-Friendly, High-Impact Smart Learning for Smart Professionals

CORPORATE TRAINING

Available Onsite / Online Team-Based Learning, Your Way Tailored for Business Goals Training That Grows With Your Team On-Demand Expert Instructors

Can’t find the right Learning Mode?

Our instructors

Mohammad Gufran Network Binary

MOHAMMED GUFRAN

17 years of Experience
Enterprise Networking | Network Security | Software Defined Networking & Automation

AKMAL YAZDANI

18+ years of Experience
Azure & AWS services |Managing and Implementing Windows servers

MUHAMMAD MUSAB

4+ Years of Experience
Cisco Technologies | Cisco and HPE ARUBA Technologies | Routing and Switching

RANIA GABRIEL GEORGE HAKIM

25+ years of Experience
Enterprise Networking | Network Security | Software Defined Networking & Automation
Microsoft Instructor and Windows Network Specialist

MOHD FARAZ HARMIS

25+ years of Experience
Managing and Implementing Microsoft Azure cloud | Active Directory

SHAHEEN AKHTAR

17 years of Experience
TCP | and UDP protocols, along | with expertise in firewalls such as Palo Alto

KUDDOOS ALI

14+ years of Experience
Experienced Network Engineer proficient in AFC | Aruba Central | Aruba CX switches

AAMIR MASOOD

6 years of Experience
AWS Compute | AWS Storage | AWS Database | AWS Management
Faizan Ahmad IT Advisor

FAIZAN AHMAD

7 years of Experience
Software support Issue Resolution | User assistance | Microsoft Active Directory
cisco Instructor in Dubai Saad shah

SAAD SHAH

10 years of Experience
Cisco Technologies | Routing and Swtiching | Data Center | Security

Here's What People Are Saying About Cybersec Trainings

Why Network Binary Trainings?

Expertise and Reputation

Comprehensive Training Programs

Industry-Relevant Curriculum

Certification and Career Advancement

Certified & Experienced Instructors

FAQs

What is the ISC2 Certified in Cybersecurity (CC) certification?

The ISC2 Certified in Cybersecurity (CC) is an entry-level cybersecurity certification designed for individuals entering the cybersecurity profession. It validates foundational knowledge across security principles, governance, IAM, networking and cloud security, and security operations and incident response.

Do I need cybersecurity work experience to take the CC exam?

No. ISC2 states that there are no specific prerequisites or work-experience requirements for the CC certification. It is designed particularly for newcomers, career changers, students, and recent graduates.

What is the format of the Certified in Cybersecurity exam?

The CC examination uses Computerized Adaptive Testing (CAT). Candidates have two hours to complete 100–125 multiple-choice and advanced item-type questions, with a passing score of 700 out of 1000.

What topics are covered in the current CC examination?

The current examination covers five domains: Security Principles; Security Governance; Identity and Access Management (IAM) Concepts; Networking and Cloud Security Concepts; and Security Operations and Incident Response.

How do I maintain the CC certification after passing the exam?

CC holders must earn 45 CPE credits during the three-year certification cycle, with ISC2 recommending 15 CPE credits per year. CC holders must also pay the applicable US$50 Annual Maintenance Fee (AMF) each year.

Dear Learner

Take a step closer to grow and glow in your career.

loader-infosectrain

Connect with Us

Dear Learner

Take a step closer to grow and glow in your career.

loader-infosectrain

Connect with Us